Not every review is a deal. A corporate client is about to give a payroll provider its employees’ data and wants to know whether the vendor is sound. The same platform runs a vendor due diligence pack: a different playbook, the same agents, citations, review and decision record. The vendor and every figure here are illustrative.
| Engagement | Vendor review — Brightline Payroll Services Inc. (illustrative), DIL-2026-0007 |
|---|---|
| Client | Fenwick Industrial Group (illustrative), onboarding the vendor |
| Actors | Deal broker (owner), practice leader |
| Data room | SOC 2 Type II report, audited financial statements FY2025, master services agreement, certificate of insurance |
| Playbook | The platform’s vendor pack: security (SOC 2), sanctions and adverse media, financial profile, certificate of insurance, the liability cap |
| Agents involved | Data room agent works the whole playbook; report and supervisor agents run; the program agents stand aside |
| Systems touched | InsightPulse (company profile, rating, news) |
| Outcome | 5 of 6 playbook items answered, 3 findings to review; the certificate shows $3M of cyber where the MSA requires $5M |
The mismatch
vendor keeps cyber
of at least $5M"] --> CMP{"Certificate of insurance:
cyber $3M"} CMP -- "below" --> F["Finding (high):
certificate below
the contract"] CAP["MSA §8.1: data-breach
cap $5M"] --> F F --> ACT["Ask the vendor for
an updated certificate
or an endorsement"] style F fill:#fdecec,stroke:#e57373 style ACT fill:#e7f8f1,stroke:#10b981
Step by step
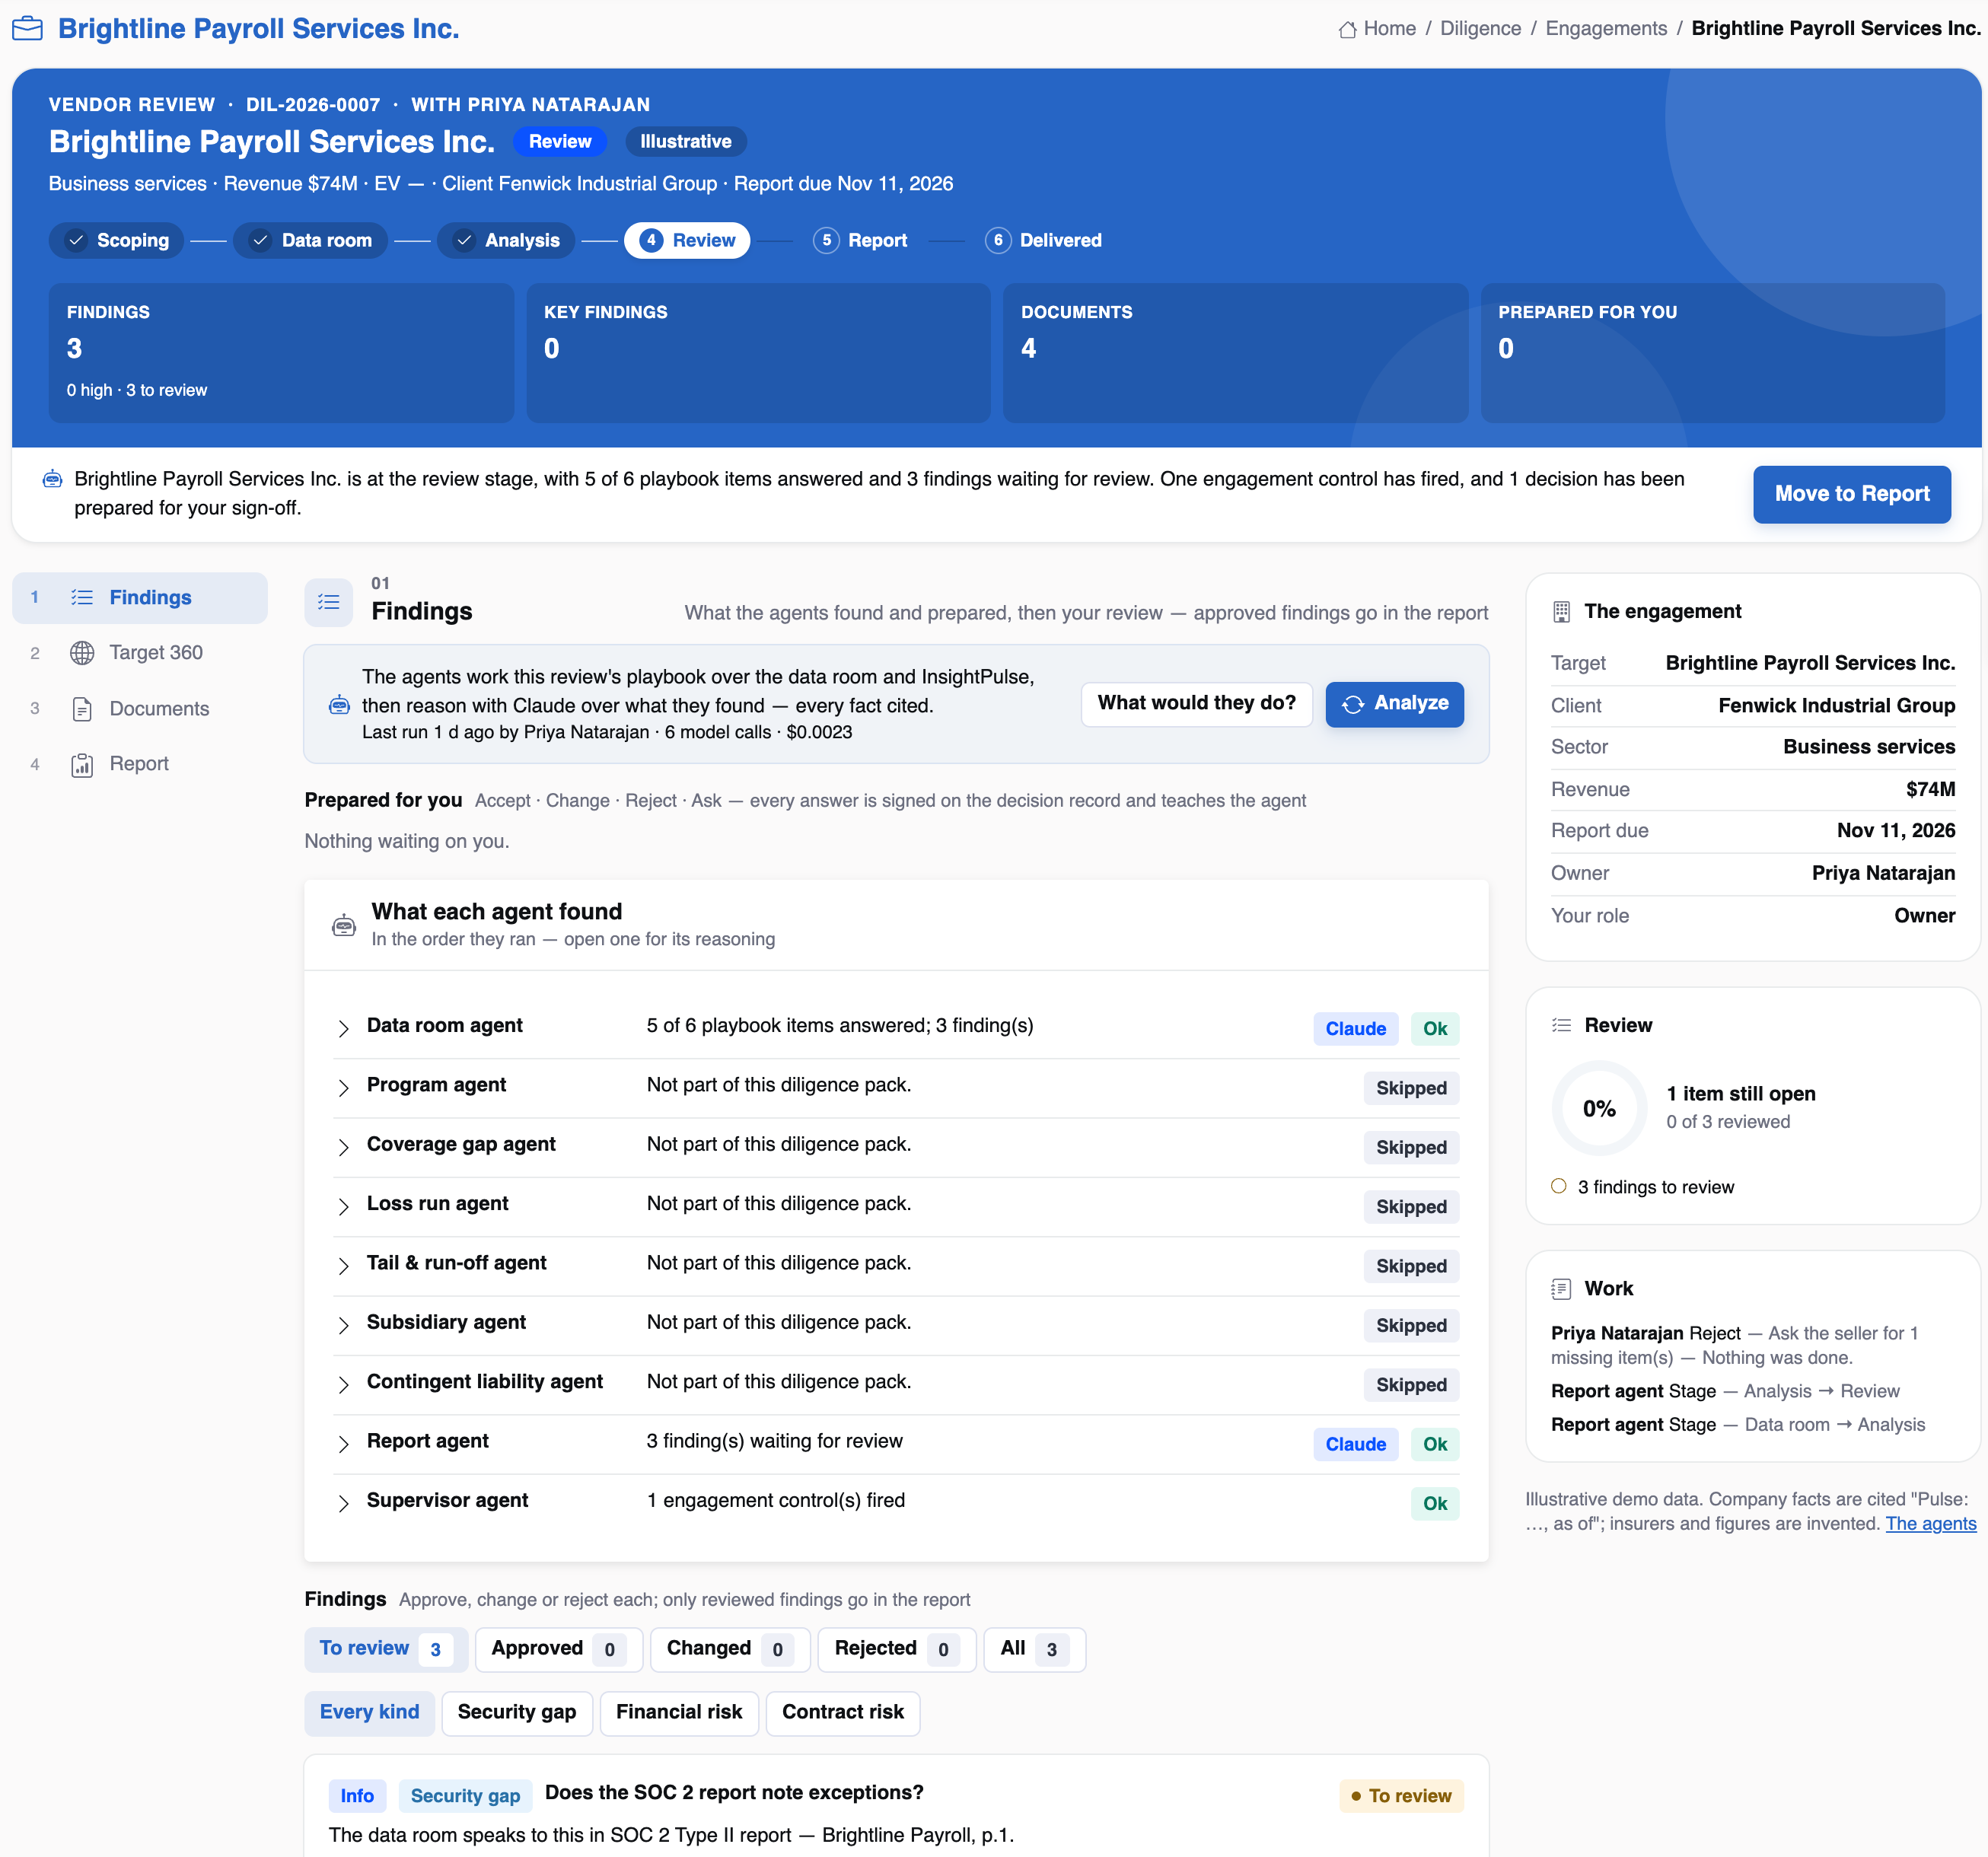
A vendor engagement uses the vendor pack. The workspace shows Findings, Target 360, Documents and Report; the program zones stand aside.
Four documents, each into cited pieces: the SOC 2 opinion and exceptions, the financials, the MSA sections, the certificate.
Works every question: a current SOC 2 (unqualified, two access-review exceptions remediated in Q1 2026); the financial profile from the statements and Pulse; the liability cap (twelve months’ fees, $5M for data breach); the certificate (cyber $3M).
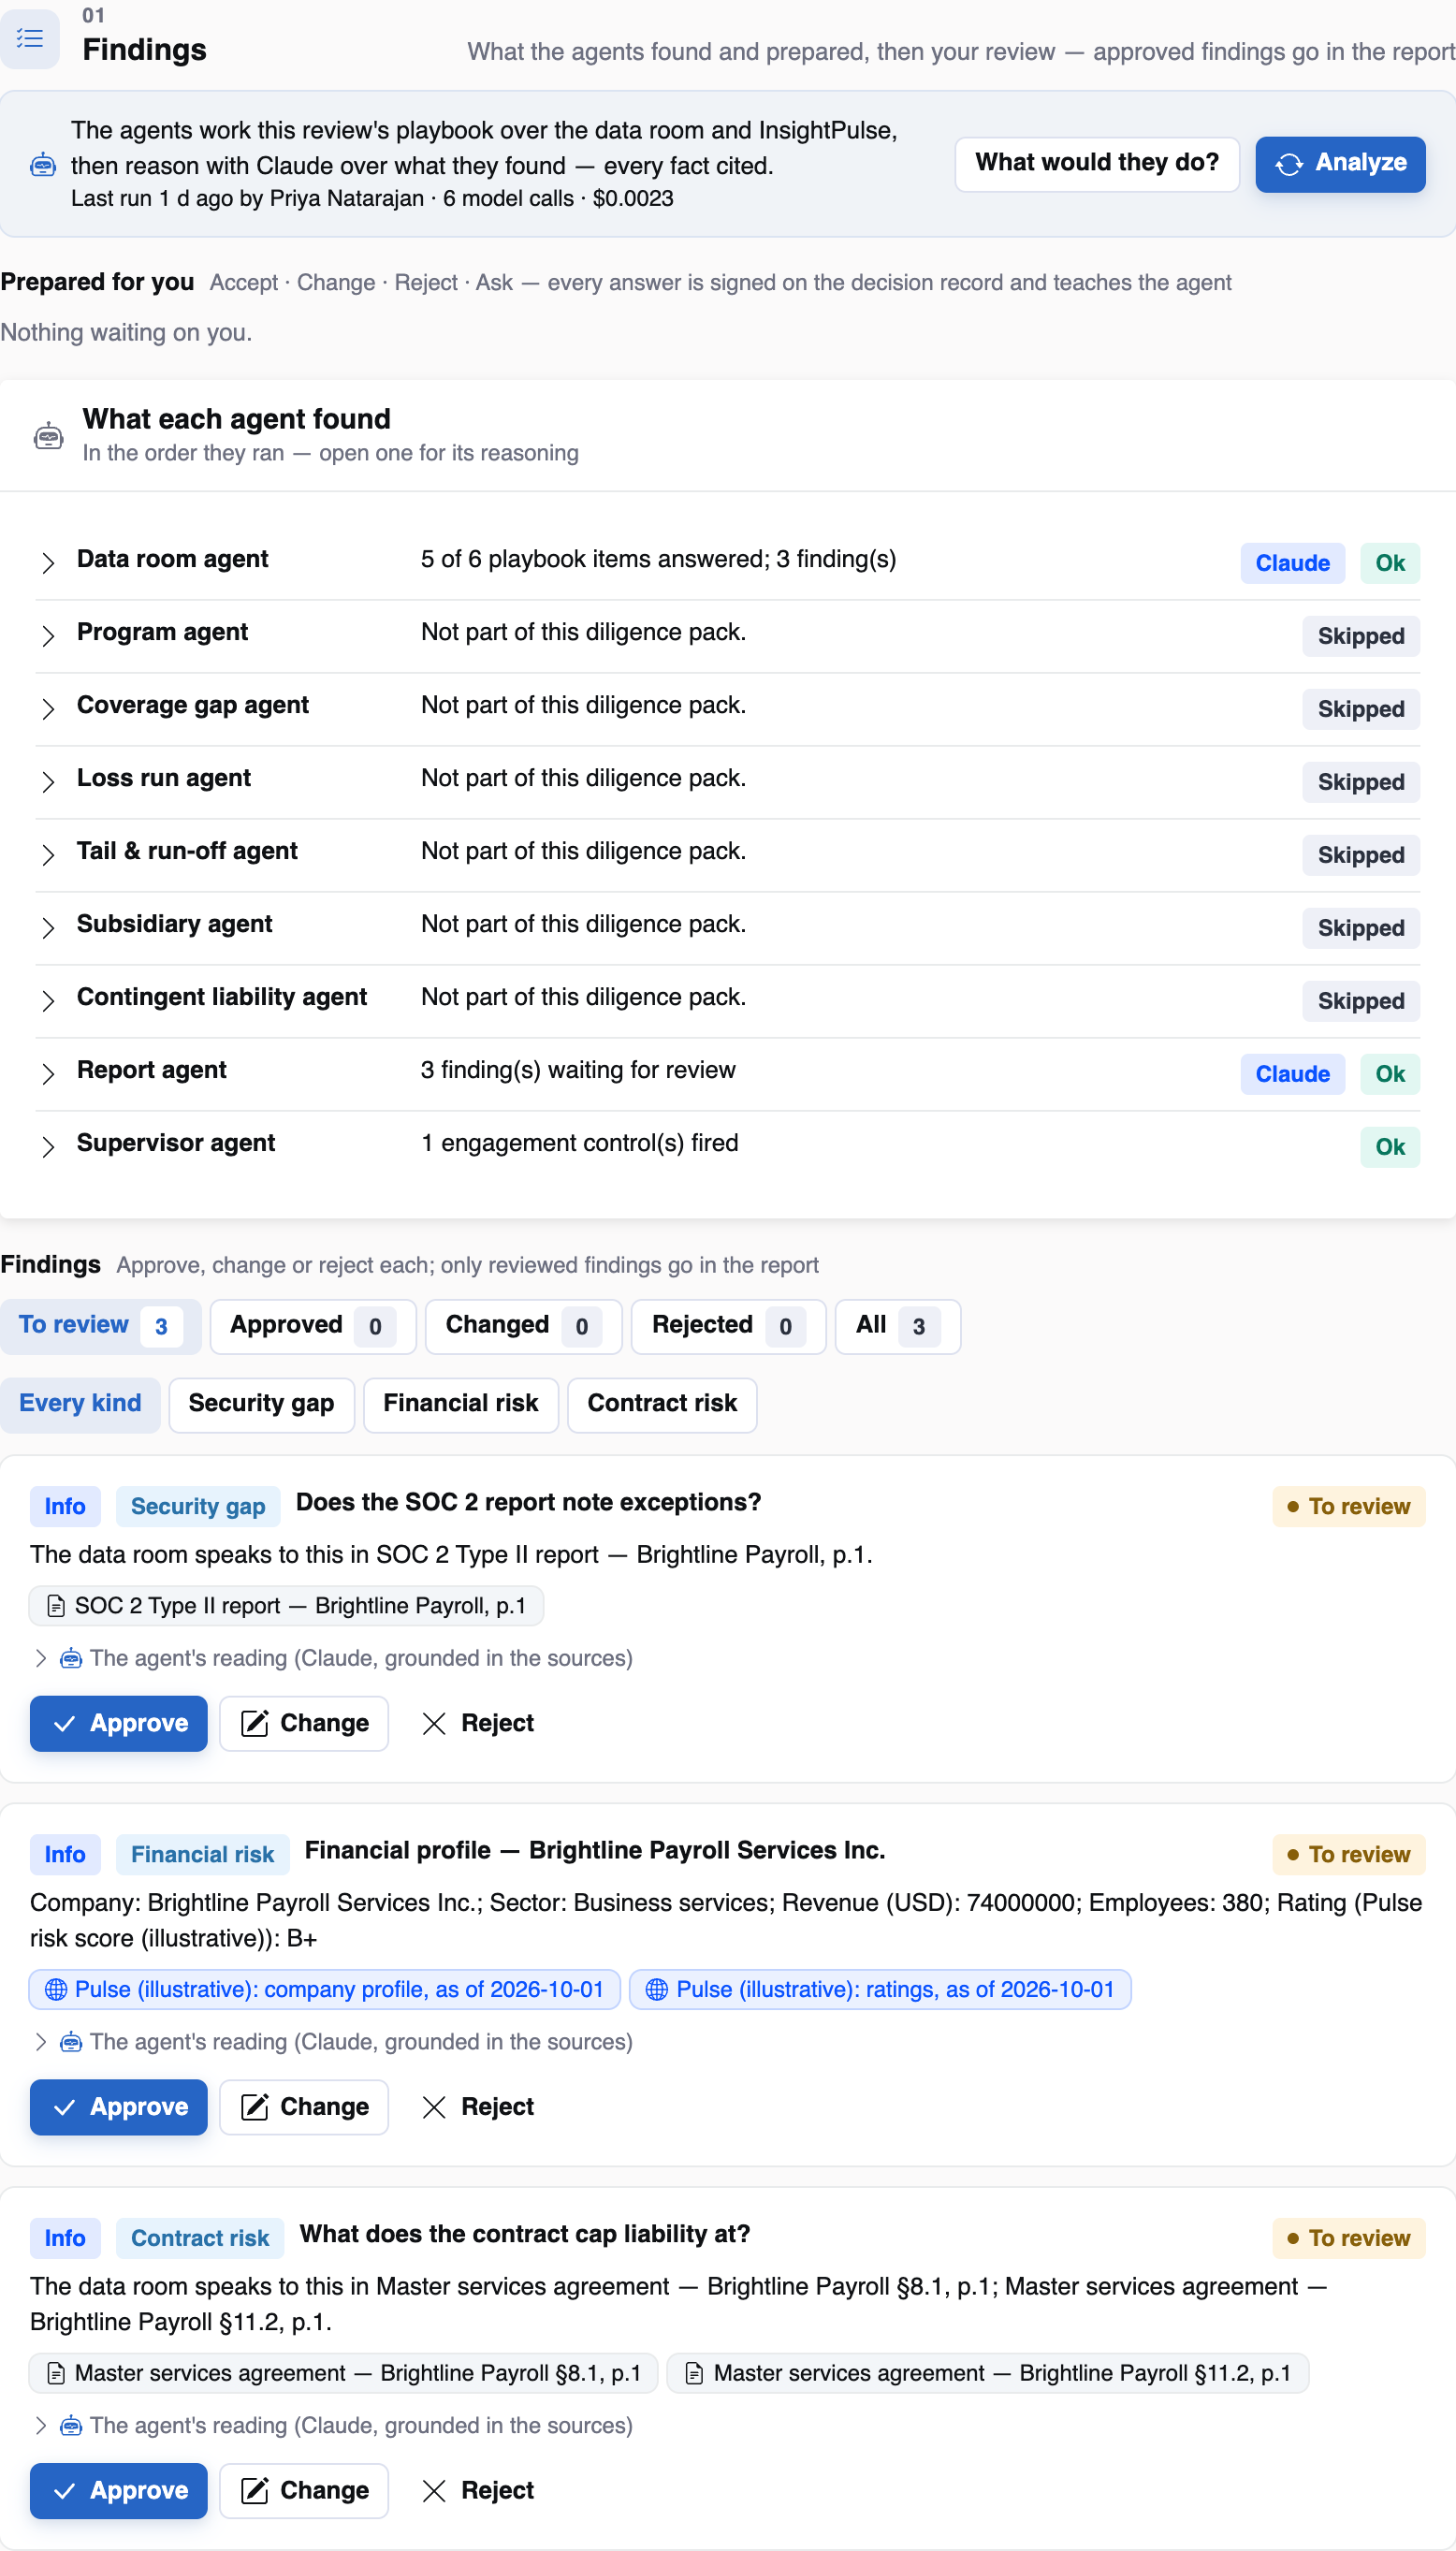
Three findings waiting for review.
One engagement control fires; the run is written to the decision record.
Approves the certificate finding as the one that matters, notes the customer concentration (top three clients are 31% of revenue) as low, and asks the vendor for an updated certificate.
The report is built from the reviewed findings and delivered to the client.
The screens
Who talks to whom
| Agent | What it prepared | What it cites | Who decides |
|---|---|---|---|
| Data room | SOC 2 Type II: unqualified; two access-review exceptions, remediated | SOC 2 Type II report, p.1 | Broker |
| Data room | Liability capped at twelve months’ fees; data breach capped at $5M | MSA §8.1, p.1 | Broker |
| Data room | Certificate shows $3M cyber; the MSA requires $5M | Certificate of insurance; MSA §11.2 | Broker |
| Data room | Financial profile: revenue, EBITDA, customer concentration | Audited financial statements; Pulse: company profile | Broker |
| Program agents | Not part of this diligence pack | — | — |
One platform, any pack
The diligence core is domain-neutral: a pack brings its document categories, playbook, finding categories, report template and rules. A practice can run insurance program reviews and vendor reviews in one place, with one review discipline and one record.
Edge cases
| What happens | What InsightDueDiligence does |
|---|---|
| The SOC 2 report is older than a year | “Is there a current SOC 2 report?” is answered no, and the finding asks for a bridge letter. |
| Pulse has adverse media on the vendor’s parent | It is a finding citing Pulse with its date; a person decides what it means. |
| The vendor sends a new certificate | Add it to the data room and Analyze; the earlier run stays on the record. |
On the deal desk
Four documents, six questions, three findings, one that matters. The review takes minutes, not an afternoon.
For IT & architecture
The vendor pack is a manifest of categories, questions, checks and rules; the agents and workspace are the same code.
For practice leaders
A contract requirement checked against a certificate, with both cited, is the kind of control an auditor asks for.
Questions we get asked
Is sanctions screening done here?
The playbook asks whether the vendor or its parent is on a sanctions list or in adverse media, answered from InsightPulse. It is a diligence question, not a payments-grade screening service.